Defending the Mission 24×7
Partner Technologies Used
ThreatDefender, Managed Security, Threat Detection and Response, Microsoft Defender, Microsoft Sentinel, Microsoft Entra ID
Project Highlight
24×7 threat monitoring, rapid incident response, and continuous security improvement helped Medical Teams International protect global humanitarian operations without building an internal security operations center.
In This Case Study
- Because the Mission Can't Stop
- The Cybersecurity Challenge of a Global Nonprofit
- Building 24x7 Security Operations With ThreatDefender
- Results
- Continuous Security Improvement Beyond Incident Response
- Enterprise Security Expertise Without Enterprise Costs
- Advice for Other Mission-Driven Organizations
- The Outcome
Because the Mission Can't Stop
Medical Teams International operates where many organizations would not.
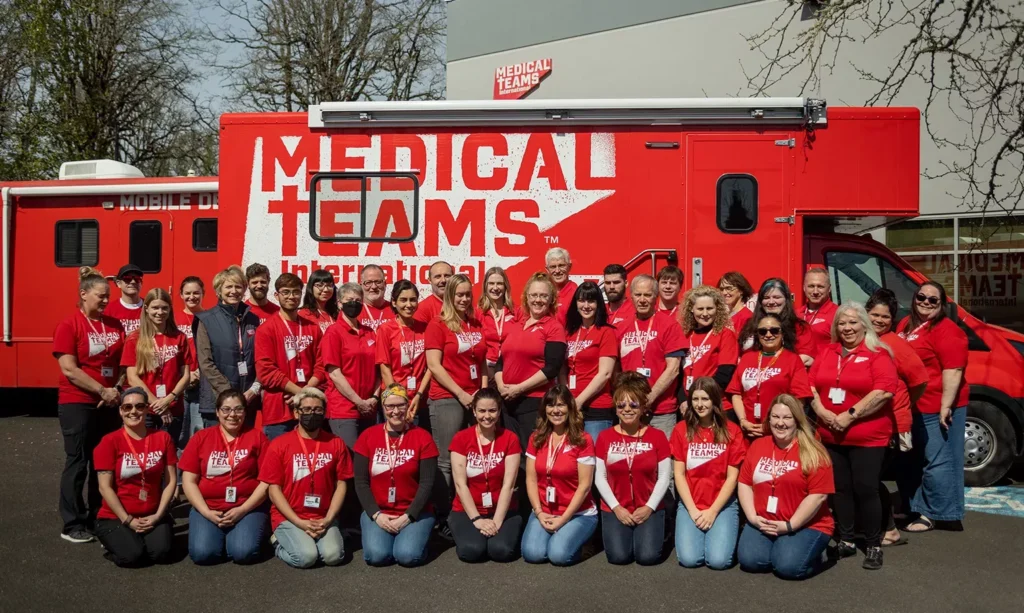
The nonprofit delivers life-saving medical care, training, and support to vulnerable communities around the world. MTI hires and trains their own staff while partnering with Ministries of Health in remote countries to serve the forgotten.
Infrastructure Manager Jeff Simmons explains, “We provide life-saving medical care at refugee camps, including education, training, and medical assistance. I love our mission!”
As they address global crises, MTI can’t be interrupted by cyber incidents.
Their teams often work in difficult conditions where access to infrastructure, technology, and healthcare is limited. These conditions are tough on the team members, as IT team member Jeremy Smith explains. “Every day of their life is in jeopardy in the Sudan, in Ethiopia, in Uganda, and Ukraine, treating patients and driving convoys across areas with no roads.”
Jeff and Jeremy’s lean technology team supports that life-saving mission and more. Responsible for connecting and protecting users operating across multiple continents, time zones, and risk environments.
"We are a small team with a lot of responsibility," acknowledges Jeremy.
The Cybersecurity Challenge of a Global Nonprofit
Like most nonprofit organizations, Medical Teams International faces growing cybersecurity threats without the luxury of unlimited resources.
The organization lacked dedicated security personnel, yet supported operations spread across the globe. “One of the things that makes us different is that we hire our medical professionals from the areas in which they work. Even after we’re gone, they will remain,” explained Mr. Simmons. With most of its workforce in Africa, there’s a significant time-zone gap between users in the field and the IT staff in the United States.
At the same time, the threats continue to hit hard.
Jeff outlined the scale, saying:
"We get hit with threats constantly, multiple incidents per day. Some of them benign, some of them false positives, some of them real."
The problem was not simply detecting threats. It was determining how a lean IT team could effectively respond to them around the clock.
Mr. Smith framed the core question the team had to address, asking “How do we, in today’s world, effectively deal with cyber threats in our environment in the most affordable and productive way we can?”
“How do we, in today’s world, effectively deal with cyber threats in our environment in the most affordable and productive way we can?”
Jeff Simmons (Infrastructure Manager, Medical Teams International)
Building a SecOps Capability Without Building a SOC
Medical Teams International turned to eGroup’s ThreatDefender service to gain the expertise, visibility, and 24×7 monitoring capabilities needed to protect its environment.
Rather than purchasing another tool, the organization effectively extended its team.
Jeremy said:
"It's evolved into a really great partnership with the eGroup. We consider them part of our team, definitely."
Today, eGroup’s ThreatDefenders continuously monitor the environment, investigate suspicious activity, block malicious behavior, create incident tickets, assist with remediation, and provide configuration assistance to strengthen security over time.
For Jeff, the value is straightforward.
“It's really helping to solve the problem of being barraged constantly with threats. eGroup does a great job of stopping incidents either through automations or human interaction, creating tickets to notify us, making sure that we've seen and responded to the tickets, and taking action appropriately."
The result is enterprise-grade cybersecurity capabilities without the need to build and staff an internal security operations center.
Results
One recent example of a thwarted threat involved a device that generated multiple malicious detections. ThreatDefender identified the activity, blocked the offending IP address, and coordinated remediation actions before the situation could escalate.
In another incident, a business email compromise attack successfully breached an account and attempted to redirect financial communications. ThreatDefender immediately recognized suspicious activity and launched an investigation.
Jeff recalled:
"eGroup alerted us right away and began to shut everything down."
The attacker had granted delegated access to compromised mailboxes and attempted to hide sensitive communications in obscure folders.
Fortunately, the response in both cases was immediate.
Jeff said, “Notification was within minutes,” adding that “eGroup contacted us through Teams and also called each one of us several times until they got someone to answer. It was just a matter of hours before we had gone through everything and had it locked down.”
Most importantly, the attacker was stopped before any meaningful business impact occurred. Jeff emphasized, “Nothing escaped our environment of a personal or financial nature.”
“Notification was within minutes … eGroup contacted us through Teams and also called each one of us several times until they got someone to answer. It was just a matter of hours before we had gone through everything and had it locked down.”
Jeff Simmons (Infrastructure Manager, Medical Teams International)
Jeremy believes the outcome could have been very different without a dedicated security operations team watching the environment.
"We were very fortunate. Had eGroup not noticed that strange user account...”
What could have become a costly cybersecurity incident instead became a learning opportunity. “It really opened our eyes, and there’s been growth because of that event,” Mr Smith said. “We’ve taken a lot of precautions.”
Continuous Improvement, Not Just Incident Response
Rather than simply report and remediate issues like eGroup does, both Jeff and Jeremy point to another benefit: continuous improvement.
Jeremy appreciates that the engagement goes beyond reporting metrics.
"They're focused on continuous improvement. They’re not just generating metrics to talk about."
Configuration changes are made in response to specific or global threats. Monthly security reviews provide visibility into threat activity, response metrics, emerging risks, and opportunities to strengthen the organization’s security posture.
Jeff said:
"They're always making suggestions, just little tips and tricks that we're constantly getting to harden our security."
Whether identifying stale user accounts, recommending authentication improvements, or helping deploy additional phishing protections, the focus is always proactive.
Delivering Enterprise Expertise Without Enterprise Costs
For nonprofit organizations, every dollar invested in technology is a dollar that must ultimately support the mission.
Jeremy compares ThreatDefender to the alternative of building a fully staffed internal security team. “If you had four people, what would your yearly price be for that? It would probably be in the $300,000–$400,000 a year range. It’s a cost savings for what we pay eGroup.”
For Jeff, the value goes beyond cost savings.
"I would be spread so thin trying to do what we have eGroup doing for our team. It’s like having an extra team with the breadth, and the depth of knowledge."
Perhaps Jeff’s most telling observation is also the simplest. “It’s not only cybersecurity, but it’s also peace of mind for me.”
“If you had four people, what would your yearly price be for that? It would probably be in the $300,000–$400,000 a year range. It’s a cost savings for what we pay eGroup.”
Jeff Simmons (Infrastructure Manager, Medical Teams International)
Advice for Other Organizations
Medical Teams International offers a straightforward message to other nonprofits and mission-driven organizations: Do not assume that because you haven’t experienced a major cybersecurity incident, you are secure.
Jeremy advised:
"If you've skated by now and never had a cyberattack and you feel like it's never going to happen, you should think about having a hardening test done. You're vulnerable. Don't count on your fortunes that it's never going to happen because before you know it, it's too late."
Jeff added a practical set of recommendations for organizations that want to strengthen their security posture:
"Have the conversations. Have them do penetration tests. See where you need to shore up. Having that team to back you up is key."
Outcome
Medical Teams International exists to provide life-saving care to people facing extraordinary challenges, and in doing so, needs secure, resilient technology and the confidence that cyber threats will not disrupt critical operations.
Through its partnership with eGroup, Medical Teams International has gained 24×7 security monitoring, rapid incident response, practical cybersecurity expertise, continuous improvement, and a trusted extension of its technology team.
24x7 Security Monitoring
Continuous threat detection and response
Minutes Incident Notification
Rapid escalation of critical threats
$0 Financial Loss
From the documented email compromise incident
“Your team has always been readily available, accessible, and extremely knowledgeable. That seems to be the standard for eGroup and not the exception.”
Jeff Simmons (Infrastructure Manager, Medical Teams International)
Protect Your Organization Around the Clock
Extend your security team with 24×7 threat monitoring, expert-led incident response, and continuous security improvement through eGroup ThreatDefender.