Microsoft’s Integrated Security Operations Center in Defender, now in public preview, may already be included in your Microsoft 365 E5 or E7 license. See how a free assessment checks your eligibility, Defender gaps, and Sentinel cost implications before November 15.
Is Your Organization Primed For Microsoft ISOC?
Find Out In Minutes With Our Free Readiness Assessment
On September 23, 2026, Microsoft released the Integrated Security Operations Center in Microsoft Defender (ISOC) in public preview. Microsoft positions it as a benefit for Microsoft 365 E5 and E7 customers, not as a separate product.
Microsoft’s new ISOC in Defender brings SIEM, XDR, threat intelligence, automation, and AI into a more unified Defender experience, giving security teams more of the technology they need to run a modern SOC.
For many organizations, this means a full set of security operations tools may already be part of a license they own. Supported Defender log sources come in without separate ingestion. Starting November 15, 2026, included retention grows from 30 days in preview to 90 days, covering Defender data, Azure activity and Office 365 activity.
That’s good news, but it raises practical questions:
- Does Our Licensing Qualify, & When?
- Is Our Defender Environment Configured To Get Value From ISOC?
- We Already Run Microsoft Sentinel. Should We Stay On Sentinel, Or Move To ISOC?
To help you answer them, we built an ISOC Readiness Assessment.
What Is An ISOC Readiness Assessment?
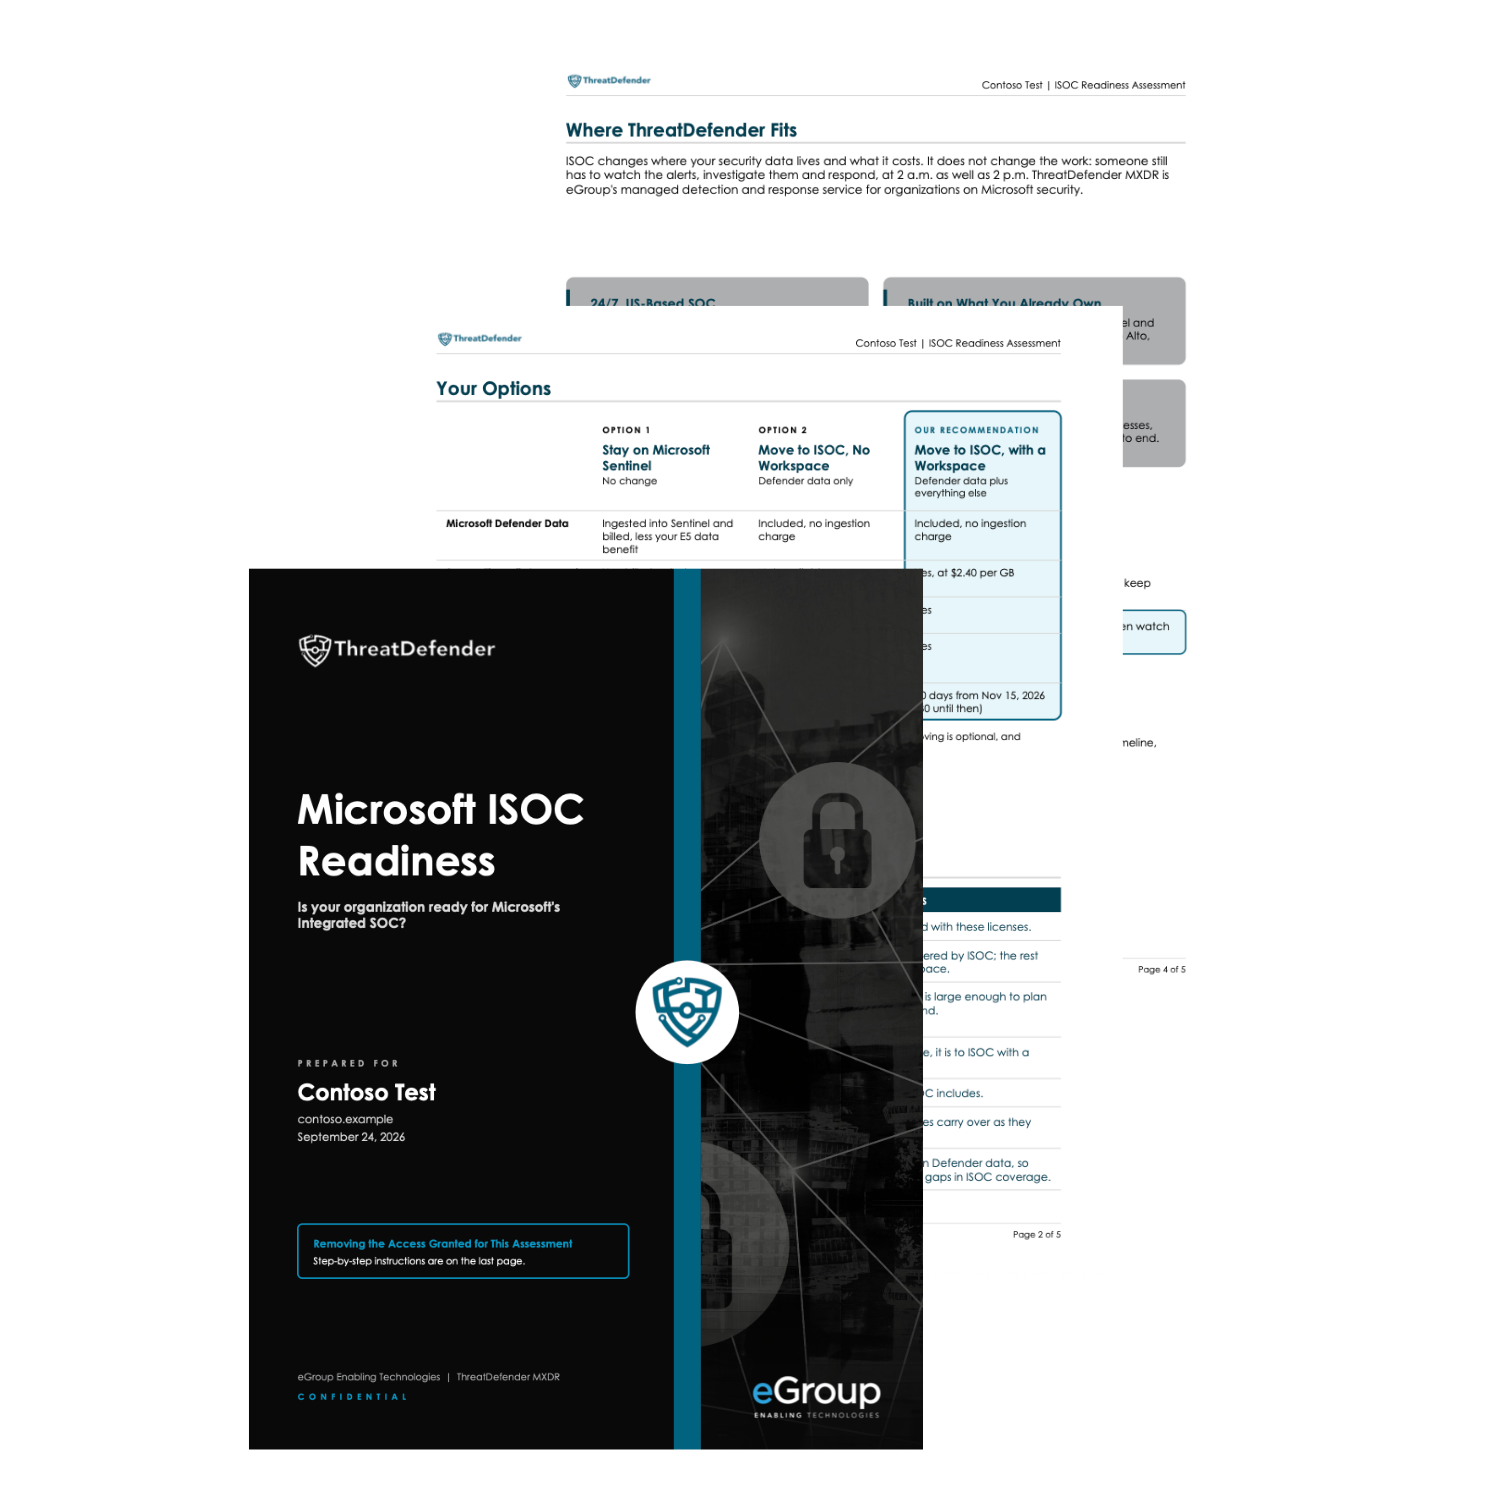
The ISOC Readiness Assessment is a free, automated assessment that shows where your Microsoft 365 environment stands. It helps you understand your eligibility for Microsoft’s Integrated SOC in Defender (ISOC), uncover security gaps, and explore potential Microsoft Sentinel cost implications.
You’ll receive a downloadable PDF report based on your Microsoft 365 tenant’s licensing, security configuration, and relevant usage data. Each finding is supported by information from your environment, with eGroup’s recommendations to help you plan your next steps.
What You’ll Find In The Report
- Microsoft Sentinel Cost Comparison.
If you’re using Microsoft Sentinel, compare your current ingestion costs with the ISOC model using your environment’s actual data volumes. - Eligibility Verdict.
Find out whether your current Microsoft licensing qualifies for ISOC now, after November 15, or not yet, with recommended next steps for each scenario.
- Readiness Score.
See how your environment measures up across six areas: licensing, Defender deployment, security configuration, data, detections, and operations. - Security Gaps & Priorities.
Identify gaps in Microsoft Defender coverage and configuration, uncover Secure Score improvement opportunities, and prioritize findings based on their potential impact.

A Note For Current Sentinel Customers
If you run Microsoft Sentinel today, nothing changes automatically. Starting November 15, 2026, existing Sentinel customers can choose to move to ISOC if their licensing qualifies. Microsoft hasn’t yet published how a move works, so the decision should rest on your own numbers.
ISOC can lower ingestion costs for Microsoft data. How much depends on your data mix. Non-Microsoft data, such as logs from firewalls, network devices and servers, still needs a workspace. In an ISOC workspace, it’s billed at Microsoft’s pay-as-you-go rate of $2.40 per GB, available since October 1, 2026 (regional pricing and other terms may vary). The assessment’s cost comparison uses your actual volumes, so you can decide to stay, or move based on facts.
How It Works
No software installation or manual security questionnaires required.
- Submit Your Information. Complete the short form to begin your free ISOC Readiness Assessment.
- Sign-In With Microsoft. Use your Microsoft work account to authorize the assessment. Administrator approval may be required, depending on your permissions.
- Review Your Environment. The automated assessment checks Microsoft licensing, Defender settings, and Sentinel configuration where applicable. Only configuration details, settings, and counts are accessed, with progress displayed as the scan runs.
Access is read-only, and none of your content is accessed.

The Other Half Of The Equation:
Who’s Manning The SOC?
ISOC gives eligible organizations powerful security tools, but tools don’t watch themselves.
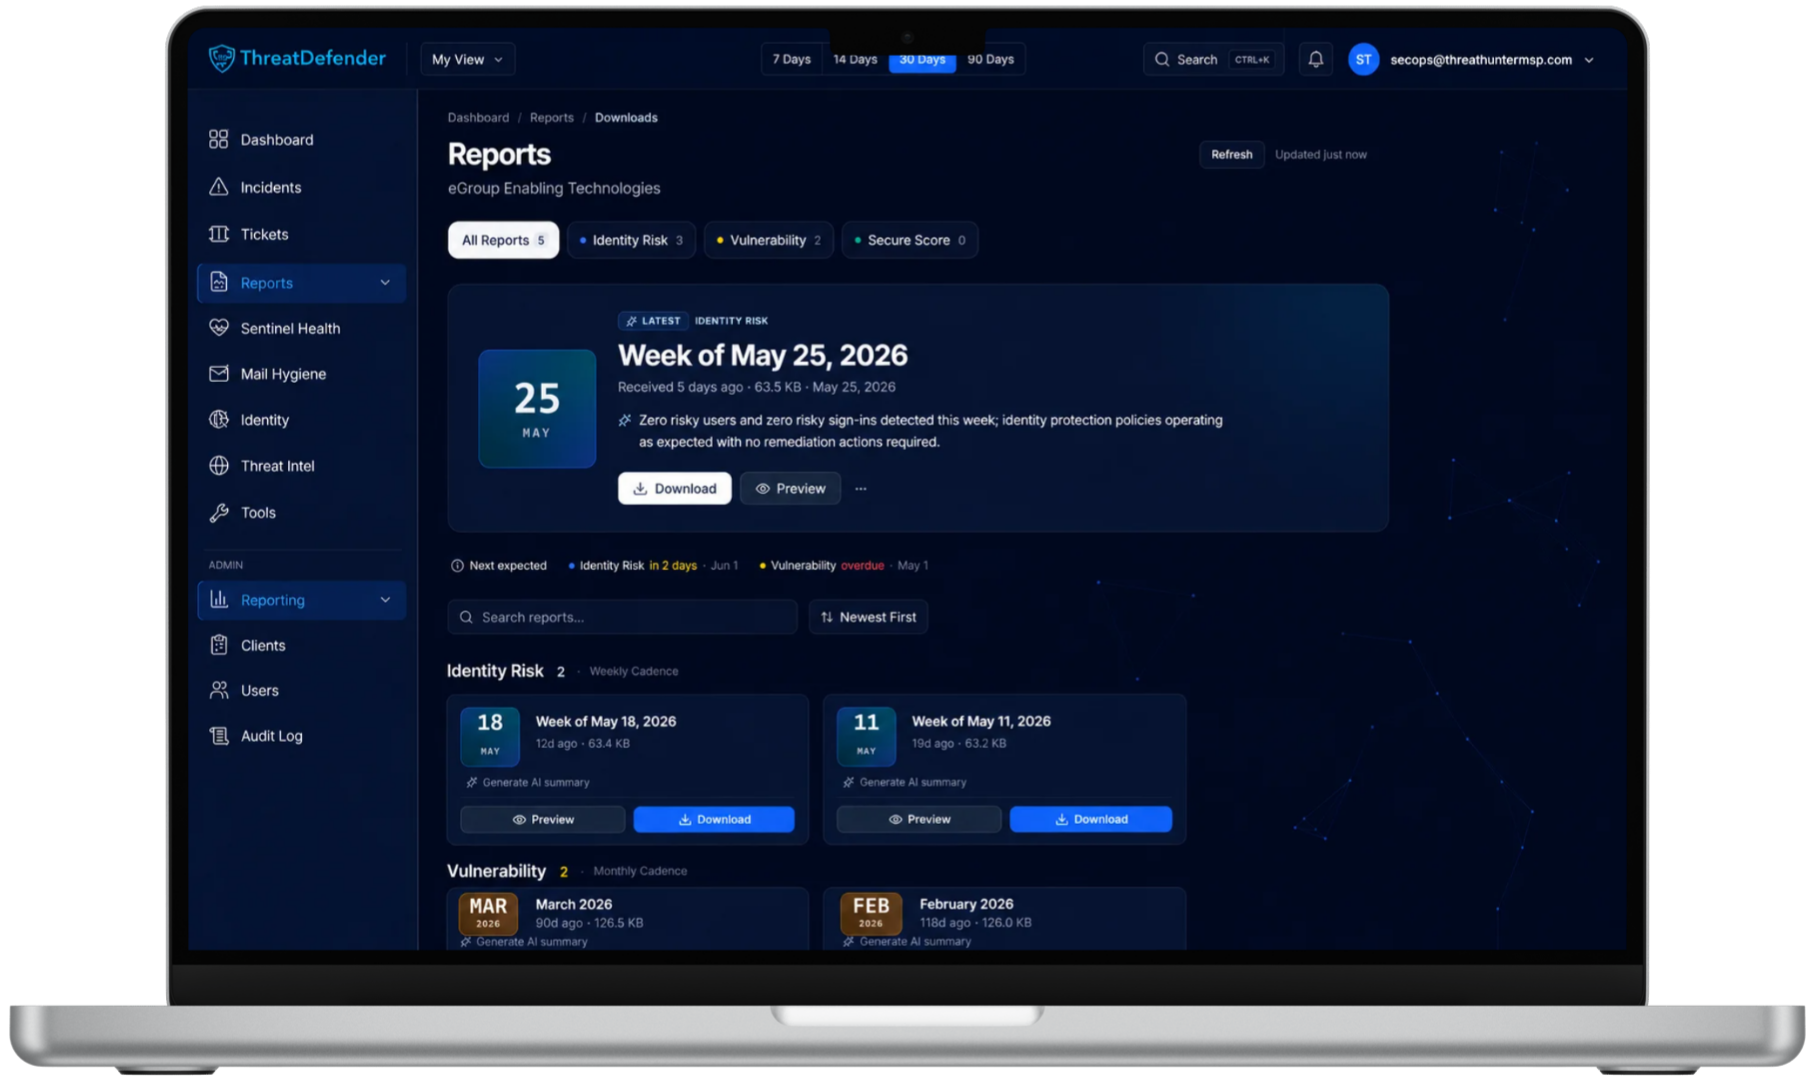
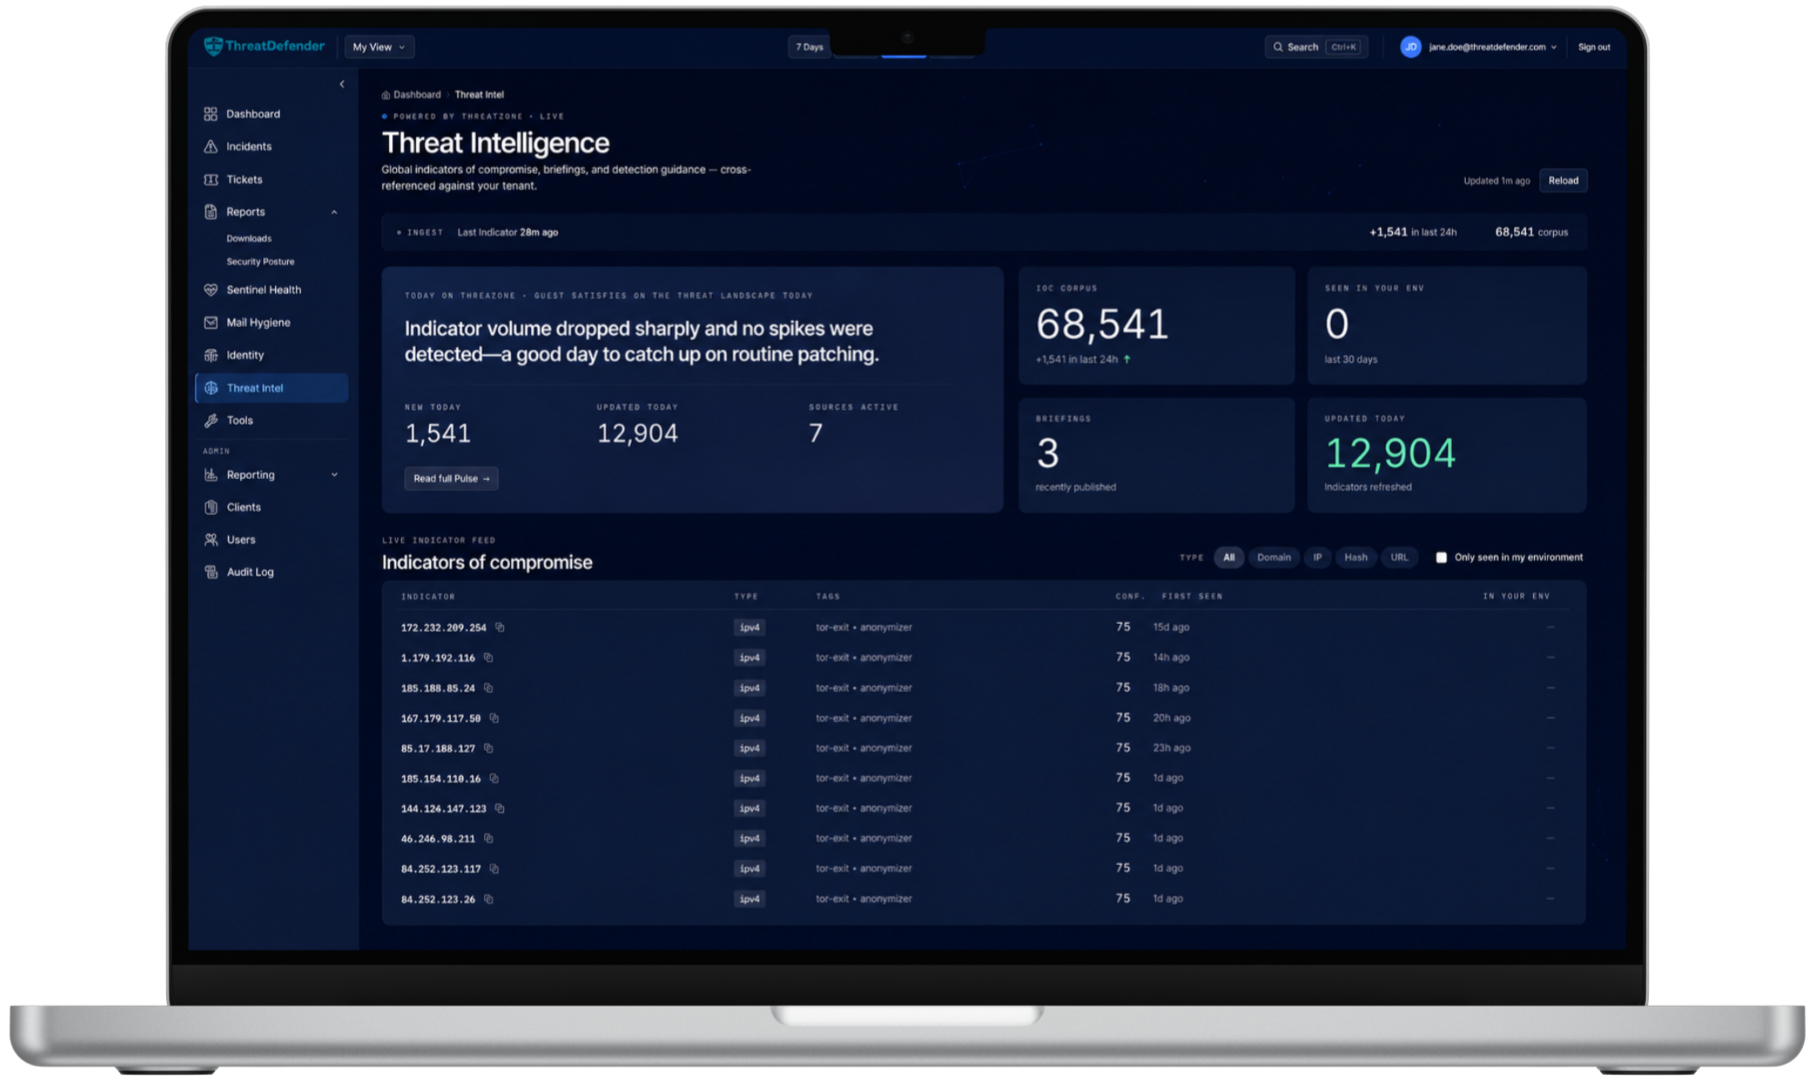
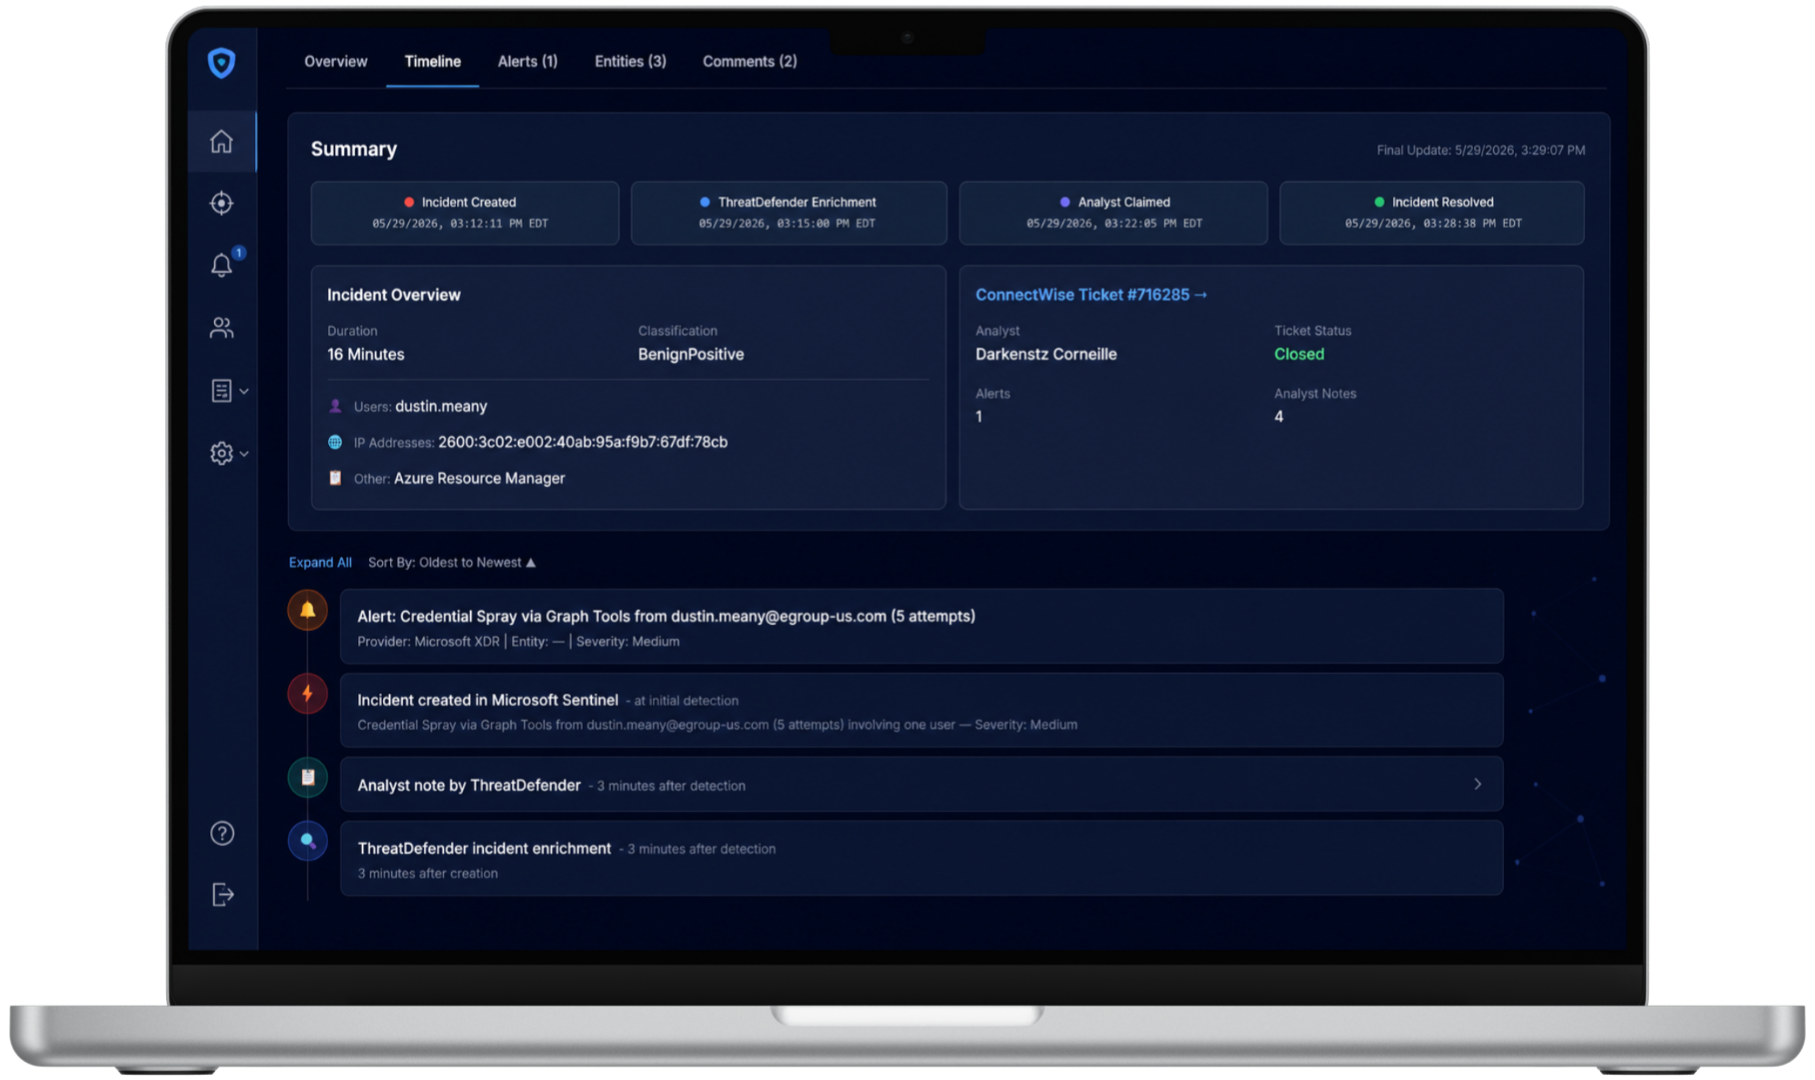
eGroup’s ThreatDefender MXDR + SARA helps solve the other half of the equation: who’s watching it, investigating incidents and responding to them. It builds on your Microsoft security investment with 24×7 eGroup analysts and SARA (our Security Analysis & Response Agent), bringing human-led investigation and response together with AI-assisted incident analysis.
Our 100% U.S.-based Security Team monitors 24x7x365. SARA organizes summaries, evidence and timelines. eGroup analysts validate the findings and make every response decision.
ThreatDefender also connects and monitors third-party sources such as Palo Alto and Cisco alongside your Microsoft data. It requires no added Microsoft licenses.
Why eGroup?
eGroup is a Microsoft Solutions Partner in the Security solution area. We hold advanced specializations in Threat Protection, Cloud Security, Identity and Access Management, and Information Protection and Governance. We’re a member of the Microsoft Intelligent Security Association (MISA) and a 9x Microsoft Partner of the Year recipient.


Get Your Free Assessment
November 15 is when 90-day retention begins and qualifying Sentinel customers can start moving to ISOC. Knowing where you stand before then will help you plan.